Examples

What WikiFix found in the Apache Kafka docs and improvement proposals

cwiki.apache.org · 1,629 pages scanned · 168 places where pages disagree · a sample of 10

An open-source project's wiki: design proposals, configuration names, protocols and APIs, written by many contributors over many years.

Engineering and configuration

Does Kafka's tiered storage feature support JBOD?

supports JBOD
JBOD support: Tiered storage feature also works in clusters configured with multiple log directories (i.e.
– Kafka Tiered Storage GA Release Notes
does not support JBOD
… storage. Topic created with the effective value for remote.storage.enable as true, can not change its retention policy from delete to compact. It does not support JBOD feature with tiered storage. Proposed Changes High-level design RemoteLogManager (RLM) is a new component which receives callback events for leadership changes and stop/delete …
– KIP-405: Kafka Tiered Storage

The release notes and the design doc disagree on a deployment constraint.
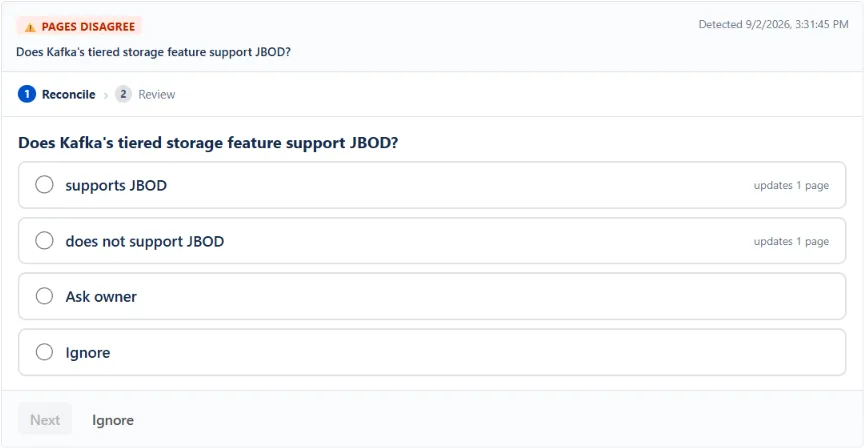
WikiFix finding: "Does Kafka's tiered storage feature support JBOD?" – one page says "supports JBOD", one page says "does not support JBOD". Options to pick an answer, ask the page owner, or ignore.

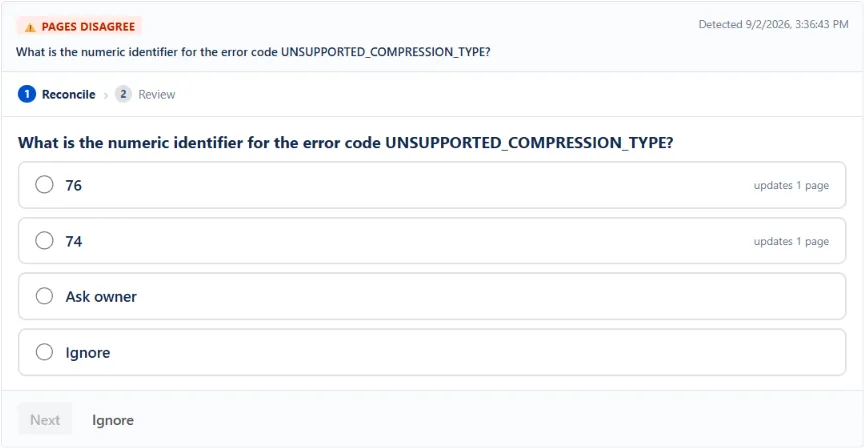
What is the numeric identifier for the error code UNSUPPORTED_COMPRESSION_TYPE?

74
It also introduces a new error code, UNSUPPORTED_COMPRESSION_TYPE (74).
– KIP-110: Add Codec for ZStandard Compression
76
… subscriptions have changed. Immediately send a GetTelemetrySubscriptionsRequest to update the client's subscriptions and get a new SubscriptionId. UNSUPPORTED_COMPRESSION_TYPE (76) Client's compression type is not supported by the broker. Immediately send a GetTelemetrySubscriptionsRequest to get an up-to-date list of the …
– KIP-714: Client metrics and observability

Two proposals give the same error code different numbers.

WikiFix finding: "What is the numeric identifier for the error code UNSUPPORTED_COMPRESSION_TYPE?" – one page says "74", one page says "76". Options to pick an answer, ask the page owner, or ignore.

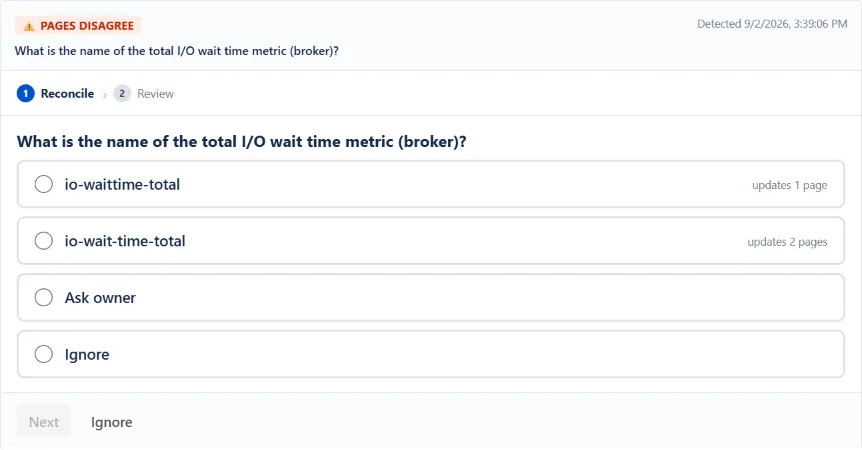
What is the name of the total I/O wait time metric?

io-wait-time-total
io-wait-ratio | io-wait-time-total
– KIP-187 - Add cumulative count metric for all Kafka rate metrics
io-waittime-total
io-wait-time-ns-total: with the same values as the current io-waittime-total
– KIP-773: Differentiate consistently metric latency measured in millis and nanos

The proposal that introduced the metric hyphenates it one way; the proposal that deprecated it says it shipped another way. A dashboard query on the wrong name returns nothing.

WikiFix finding: "What is the name of the total I/O wait time metric?" – one page says "io-wait-time-total", one page says "io-waittime-total". Options to pick an answer, ask the page owner, or ignore.

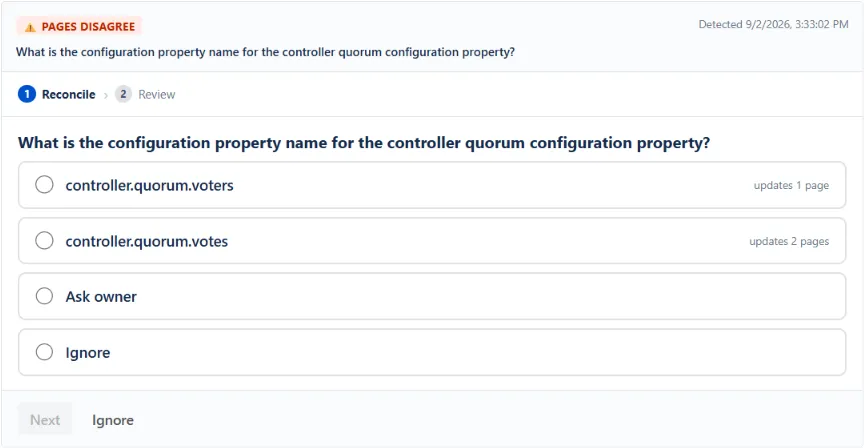
What is the configuration property name for the controller quorum configuration property?

controller.quorum.voters
… controller.quorum.voters If non-null, this must be a comma-separated list of all the controller voters, in the format:
– KIP-631: The Quorum-based Kafka Controller
For context, the set of voters in the KRaft cluster metadata partition is currently bootstrapped and configured using the controller.quorum.voters server property.
– KIP-853: KRaft Controller Membership Changes
controller.quorum.votes
… There isn't a single and trivial configuration change that enables it, but rather there are several required configurations: process.roles node.id controller.quorum.votes controller.listener.names As to the second intention, avoiding the need to distinguish between a new storage directory and a faulty one is not a good …
– KIP-785: Automatic storage formatting

A typo in a config name that every KRaft cluster needs.

WikiFix finding: "What is the configuration property name for the controller quorum configuration property?" – one page says "controller.quorum.voters", one page says "controller.quorum.votes". Options to pick an answer, ask the page owner, or ignore.

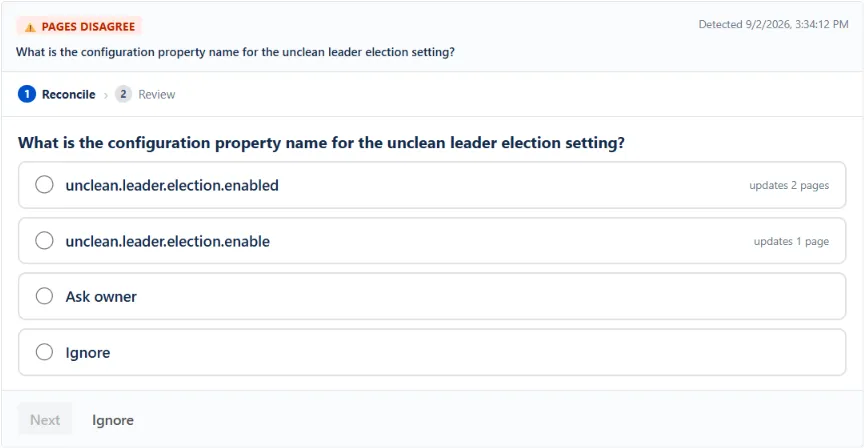
What is the configuration property name for the unclean leader election setting?

unclean.leader.election.enabled
By default Kafka runs with the setting unclean.leader.election.enabled=true.
– KIP-106 - Change Default unclean.leader.election.enabled from True to False
unclean.leader.election.enable
… set at the broker level, ensuring consistent behavior across the cluster. Public Interfaces Proposed Configurations to Enforce min.insync.replicas unclean.leader.election.enable message.max.bytes log.message.timestamp.type log.cleanup.policy compression.gzip.level compression.lz4.level compression.type compression.zstd.level …
– KIP-1210: Disallow Configurations at the Broker Level
… message.timestamp.difference.max.ms, log.message.timestamp.before.max.ms, log.message.timestamp.after.max.ms, message.timestamp.type, unclean.leader.election.enable, min.insync.replicas mirror.topics.include A comma-separated list of regex patterns for topic names to include in mirroring. Topics on the source …
– KIP-1279: Cluster Mirroring

The proposal that changed the default spells the setting differently from the proposals that reference it.

WikiFix finding: "What is the configuration property name for the unclean leader election setting?" – one page says "unclean.leader.election.enabled", one page says "unclean.leader.election.enable". Options to pick an answer, ask the page owner, or ignore.

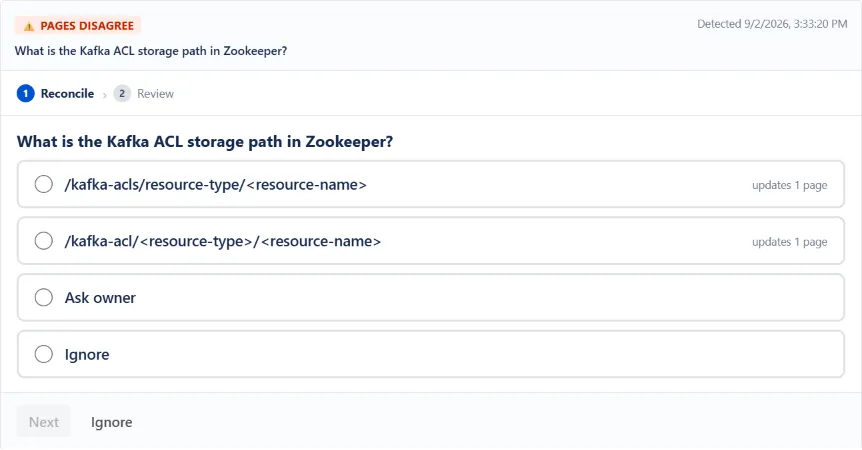
What is the Kafka ACL storage path in Zookeeper?

/kafka-acl/<resource-type>/<resource-name>
Currently, ACLs are stored on ZK under path /kafka-acl/<resource-type>/<resource-name>.
– KIP-290: Support for Prefixed ACLs
/kafka-acls/resource-type/<resource-name>
It will use zookeeper as the storage layer for acls. Acls will be stored in json format described below under /kafka-acls/resource-type/<resource-name>.
– KIP-11 - Authorization Interface

One letter in a path. The original design says kafka-acls; the later proposal says kafka-acl.

WikiFix finding: "What is the Kafka ACL storage path in Zookeeper?" – one page says "/kafka-acl/<resource-type>/<resource-name>", one page says "/kafka-acls/resource-type/<resource-name>". Options to pick an answer, ask the page owner, or ignore.

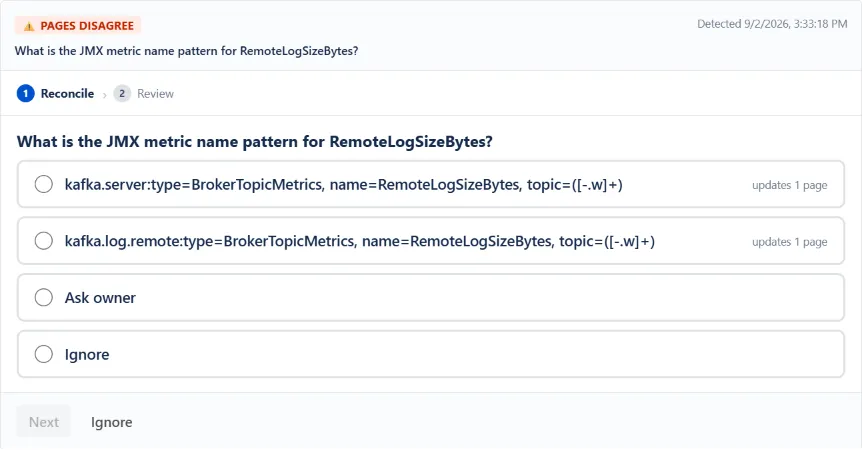
What is the JMX metric name pattern for RemoteLogSizeBytes?

kafka.log.remote:type=BrokerTopicMetrics, name=RemoteLogSizeBytes, topic=([-.w]+)
kafka.log.remote:type=BrokerTopicMetrics, name=RemoteLogSizeBytes, topic=([-.w]+) | Provides the total size of log in bytes stored on the remote tier.
– KIP-852: Optimize calculation of size for log in remote tier
kafka.server:type=BrokerTopicMetrics, name=RemoteLogSizeBytes, topic=([-.w]+)
kafka.server:type=BrokerTopicMetrics, name=RemoteLogSizeBytes, topic=([-.w]+) | The total size of a remote log in bytes.
– KIP-963: Additional metrics in Tiered Storage

Two accepted proposals put the same metric under different JMX domains.

WikiFix finding: "What is the JMX metric name pattern for RemoteLogSizeBytes?" – one page says "kafka.log.remote:type=BrokerTopicMetrics, name=RemoteLogSizeBytes, topic=([-.w]+)", one page says "kafka.server:type=BrokerTopicMetrics, name=RemoteLogSizeBytes, topic=([-.w]+)". Options to pick an answer, ask the page owner, or ignore.

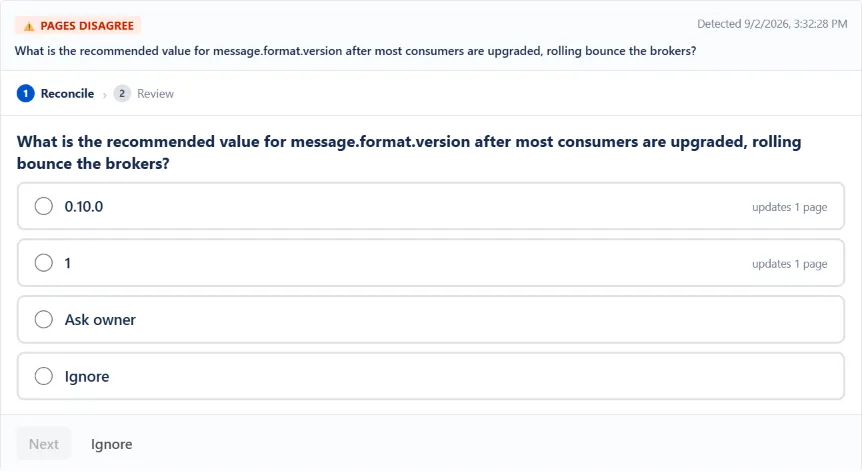
What should message.format.version be set to once most consumers are upgraded?

0.10.0
After most of the consumers are upgraded, Bump up message.format.version=0.10.0 and rolling bounce the brokers.
– KIP-32 - Add timestamps to Kafka message
1
After most of the consumers are upgraded, Bump up message.format.version=1 and rolling bounce the brokers.
– KIP-31 - Move to relative offsets in compressed message sets

Two companion proposals share the same migration step, word for word, with a different value.

WikiFix finding: "What should message.format.version be set to once most consumers are upgraded?" – one page says "0.10.0", one page says "1". Options to pick an answer, ask the page owner, or ignore.

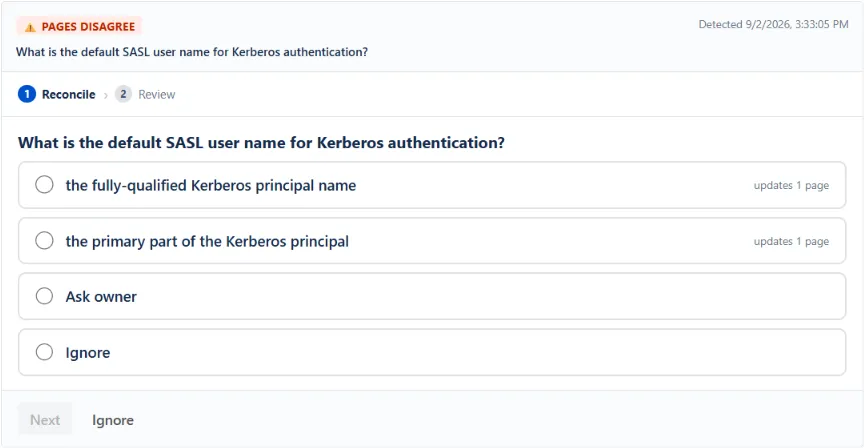
What is the default SASL user name for Kerberos authentication?

the fully-qualified Kerberos principal name
When the client authenticates using Kerberos, the user name will be the fully-qualified Kerberos principal name.
– Security
the primary part of the Kerberos principal
… "By default, the SASL user name will be the primary part of the Kerberos principal.
– KIP-203: Add toLowerCase support to SASL.kerberos.principal.to.local rule

The security overview and the current proposal disagree on the default user name.

WikiFix finding: "What is the default SASL user name for Kerberos authentication?" – one page says "the fully-qualified Kerberos principal name", one page says "the primary part of the Kerberos principal". Options to pick an answer, ask the page owner, or ignore.

Run it on your own spaces.

Your first scan produces the same kind of report for your spaces, and reading it changes nothing on your pages.